Dashboard: Users & Roles
Routerly has a role-based access control (RBAC) system for the dashboard. Users are granted permissions via roles. Three built-in roles are provided; you can create additional custom roles with any combination of permissions.
Permissions
| Permission | Description |
|---|---|
router:read | View all routers and their configuration (global: not limited by router membership) |
router:write | Create, edit, and delete routers |
model:read | View registered models |
model:write | Create, edit, and delete models |
user:read | View dashboard users |
user:write | Create, edit, and delete users, assign roles. You can only grant, edit or remove users and roles whose permissions you hold yourself; otherwise the action is refused with 403 |
report:read | View usage analytics and request logs |
settings:read | View global settings |
settings:write | Change global settings |
notification:write | Manage notification channels and rules |
token:read | View router tokens (the token list in router responses is hidden without token:read, token:write or router:write) |
token:write | Create, edit and revoke router tokens (also granted by router:write) |
role:write | Create, edit, and delete custom roles (also granted by user:write) |
audit:read | Read the audit log |
modules:read | View which modules are installed and enabled |
modules:manage | Enable and disable modules |
connections:read | View provider connections |
connections:manage | Create, edit, and delete provider connections |
resilience:read | View retry, timeout, and fallback settings |
resilience:manage | Change retry, timeout, and fallback settings |
profiles:read | View routing profiles |
profiles:manage | Create, edit, and delete routing profiles |
optimizers:read | View the optimizer catalog, samples, and previews |
optimizers:manage | Change a router's optimizer pipeline |
experiments:read | View experiments and their metrics |
experiments:manage | Create, edit, and delete experiments, manage their tokens |
Built-in Roles
| Role | Permissions |
|---|---|
admin | All permissions |
operator | Everything except user:write, role:write, settings:write, audit:read, modules:manage, resilience:* |
viewer | router:read, model:read, report:read, settings:read, token:read, audit:read, modules:read, connections:read, profiles:read, optimizers:read, experiments:read |
Managing Users
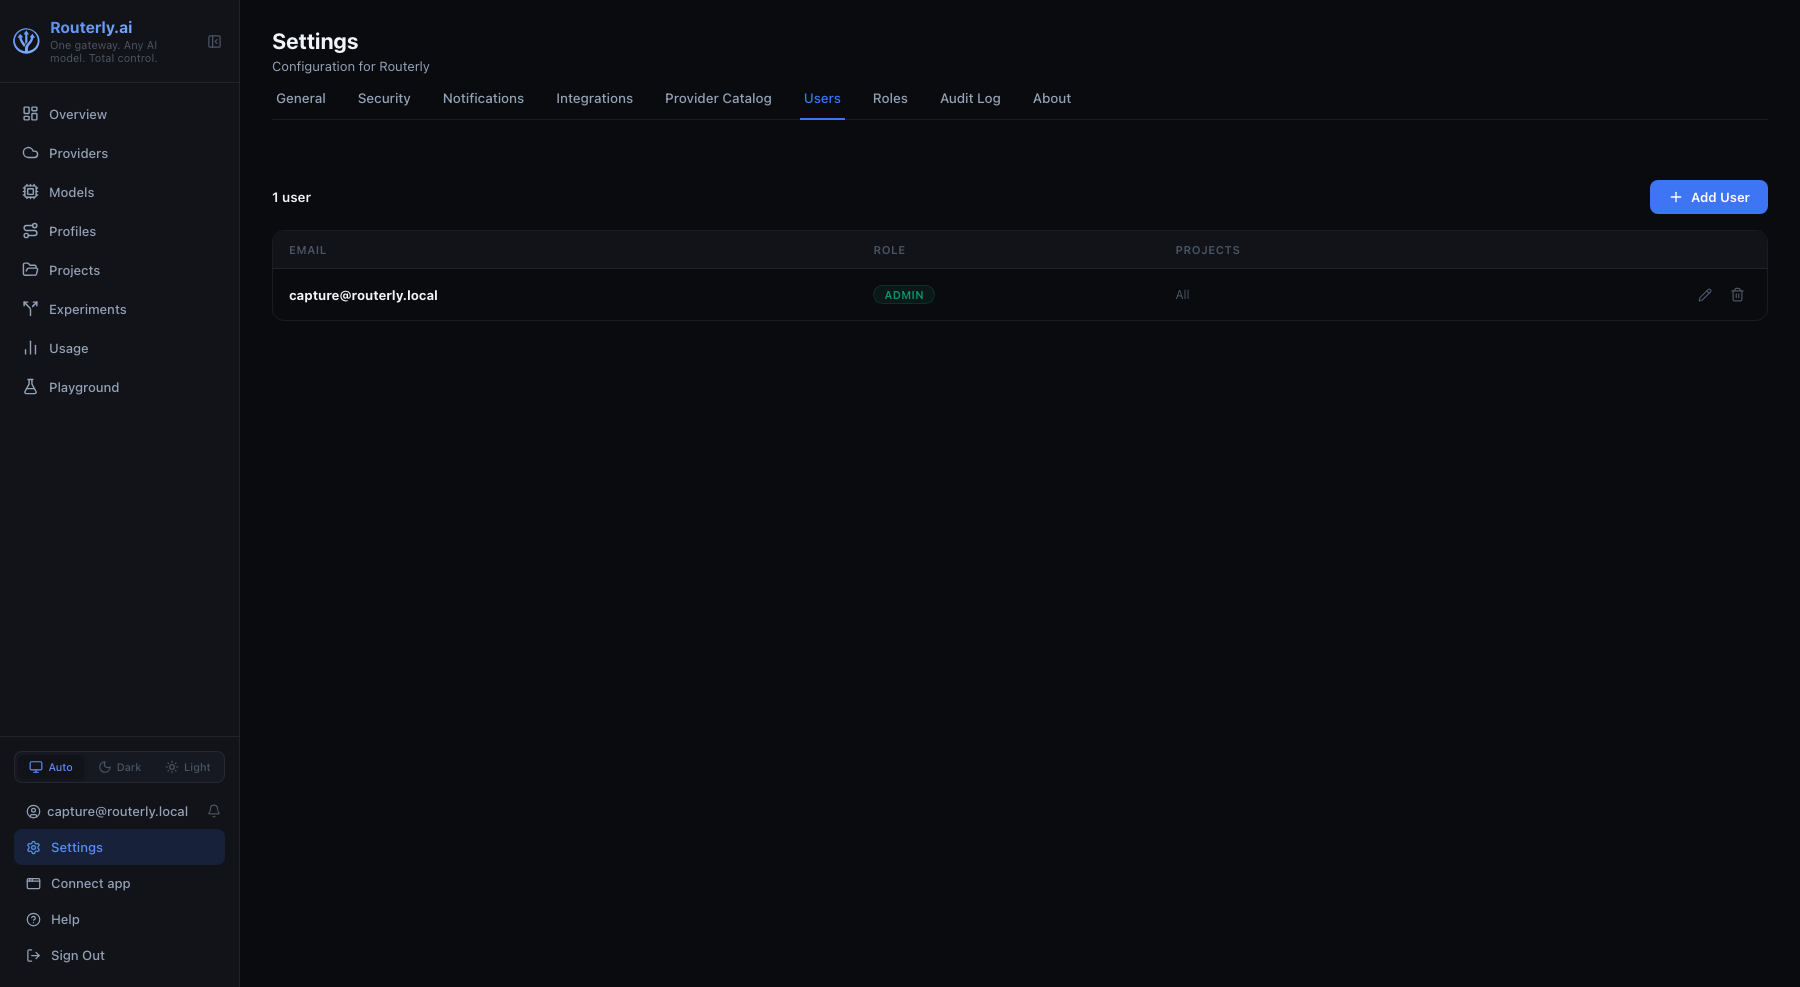
Adding a User
- Open Users in the sidebar
- Click + New User
- Enter the email address, password, and assign a role
- Click Create
The new user can log in immediately.
Editing a User
Click a row, or its Edit icon, to change the user's email, password, or
role. With user:write missing the row is inert and the icon is hidden.
Removing a User
Click the Delete icon and confirm. The user's session is invalidated immediately.
Custom Roles
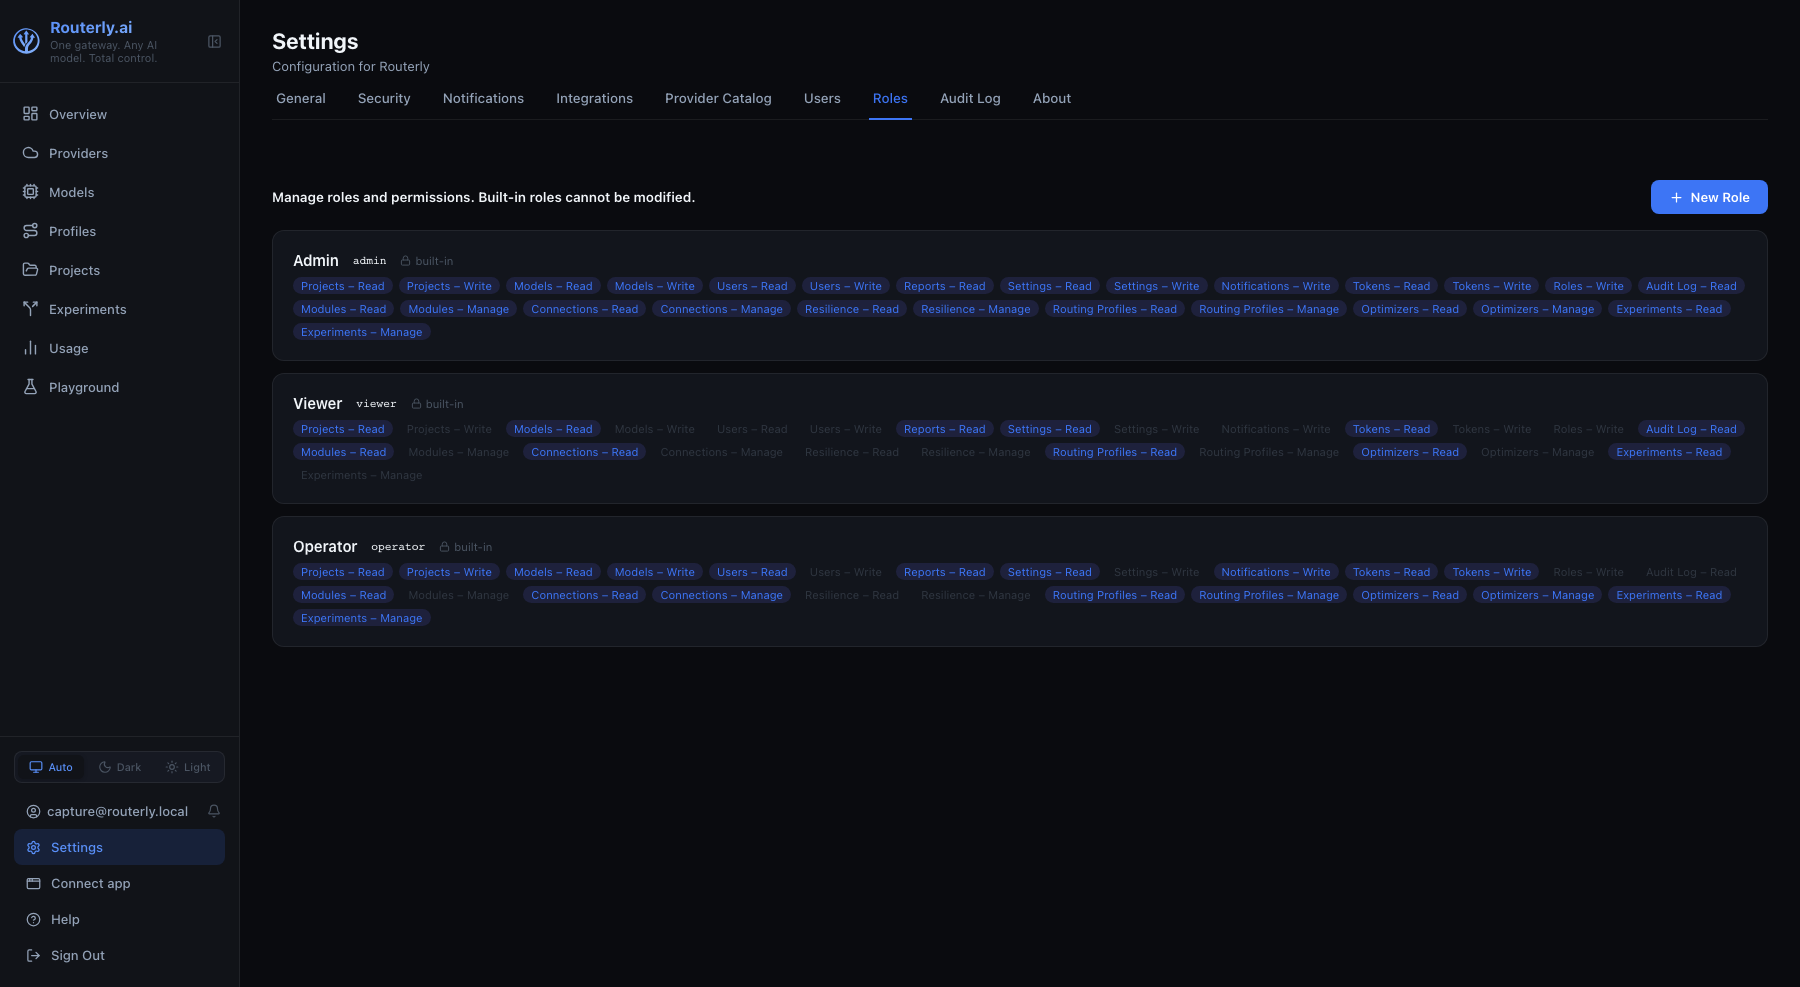
Custom roles let you define granular permission sets for specific team members.
Creating a Custom Role
- Open Roles in the sidebar
- Click + New Role
- Give the role a name (e.g.
billing_reviewer) - Check the permissions this role should have
- Click Save
Custom roles can be assigned to users the same way as built-in roles.
Editing / Deleting a Custom Role
Click Edit to change the role's permissions. Users with this role are affected immediately.
Click Delete to remove the role. Users who had this role will lose their dashboard access. Reassign them first.
Router-Level User Assignment
Users can also be assigned to specific routers (from the router's Users tab). This limits their access to that router without changing their global role.
CLI Management
# List all users
routerly user list

# Add a user
routerly user add --email [email protected] --role operator

# Remove a user
routerly user remove --email [email protected]

# List roles
routerly role list

# Add a custom role
routerly role add --name billing_reviewer --permissions report:read

# Remove a custom role
routerly role remove --name billing_reviewer